Aug. 23, 2026
First on the scene of the (cyber)crime
Okta Threat Intelligence sent its 10,000th suspicious domain notification to a customer. Most of the indicators in those notifications were not flagged by other providers at the time.
Cyber Threat Researcher at Okta
Threat intelligence Phishing Identity attacks
Currently at Okta, focused on researching identity-based threats, tracking threat actors and campaigns, and turning threat intelligence into actionable detections and protections. I also build open threat feeds now included in MISP, YETI and OpenCTI.
I am a Cyber Threat Researcher with a background spanning identity threat research, phishing investigations, incident response, threat hunting and security operations. Since 2017, I have helped international organizations in a wide range of sectors investigate, contain and remediate threats across diverse environments.
Jun. 2024 - Present
2 yrs 5 mos
Current role
 Okta
Cyber Threat Researcher
Part of Okta's Identity Threat Research team, researching identity-focused threats and attacker tactics, techniques and procedures.
A few pieces of research published on the Okta Threat Intelligence blog.
See the 6 posts in ResearchOct. 2020 - Jun. 2024
3 yrs 9 mos
Citrix
 Cloud Software Group
Sr. Security Engineer
Worked in the global Security Operations Center of Cloud Software Group, the parent company of Citrix, handling 24/7 incident response, threat hunting and detection tuning.
Aug. 2018 - Oct. 2020
2 yrs 3 mos
 Banco Santander
Global SOC Security Analyst
Worked in Banco Santander's Global SOC, providing 24/7 monitoring and an on-call service to the bank's entities worldwide.
Aug. 2017 - Aug. 2018
1 yr 1 mo
 Deloitte
CyberSOC Security Analyst
Worked in Deloitte's CyberSOC, delivering managed security services for national and international clients.
I also build open security tools. I enjoy turning noisy data into practical intelligence with AI, cloud services and APIs.
Open IOC feed
Indicators shared by the security community, collected in one place
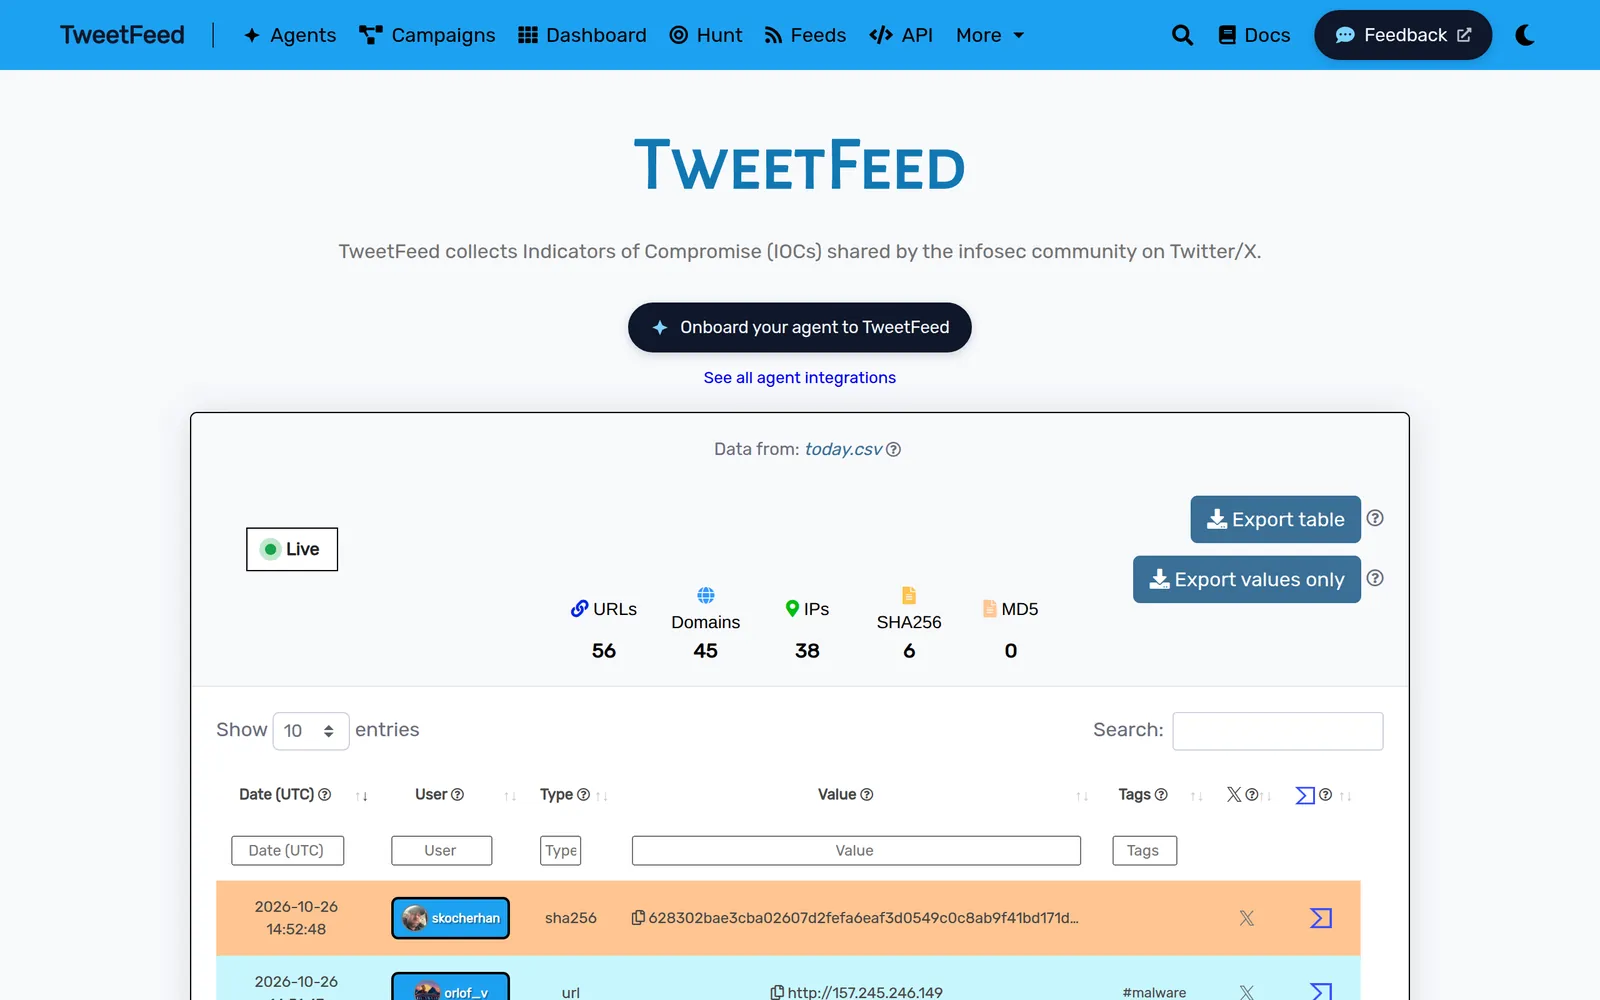
TweetFeed collects and organizes indicators of compromise posted on X. It focuses on URLs, domains, IP addresses and file hashes, and publishes them as an open feed.
694 stars on GitHub
tweetfeed.live (opens in a new tab) GitHub (opens in a new tab)
Open phishing feed
Suspicious phishing sites, captured and enriched
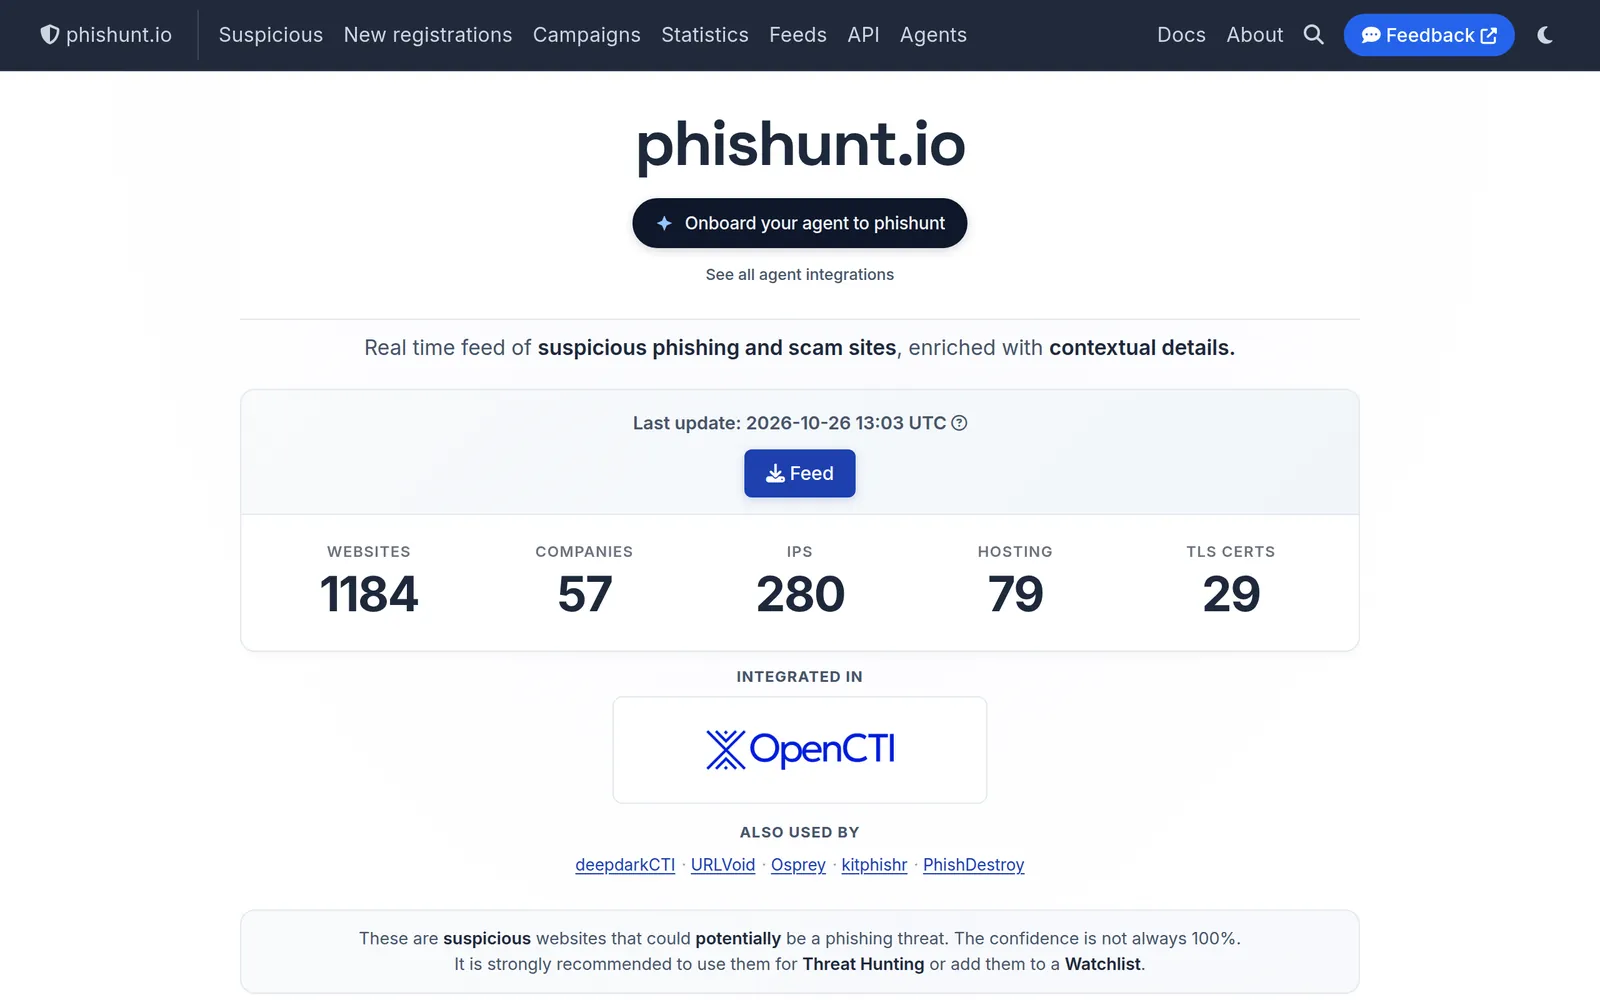
phishunt identifies and monitors suspicious phishing sites. It captures them, enriches them with hosting, certificate and network context, and publishes the results as an open feed.
286 stars on its phishing kits archive
phishunt.io (opens in a new tab) Kits archive (opens in a new tab)
A few pieces of research published on the Okta Threat Intelligence blog.
Aug. 23, 2026
Okta Threat Intelligence sent its 10,000th suspicious domain notification to a customer. Most of the indicators in those notifications were not flagged by other providers at the time.
May 2, 2026
Changes in the Tycoon 2FA phishing operation after law enforcement disrupted it in March 2026.
Dec. 19, 2025
Phishing campaigns that impersonate recruitment sites of well-known companies to steal the credentials of jobseekers.
Sep. 30, 2025
A campaign that uses the EvilProxy phishing-as-a-service toolkit for real-time phishing against users of popular enterprise apps.
Aug. 28, 2025
A large-scale phishing campaign that impersonates service providers for hotels and vacation rentals.
Jun. 19, 2025
Deceptive CAPTCHA pages that distribute a range of malicious payloads, including Redline Stealer.
Pull requests I wrote so that TweetFeed and phishunt work inside open source threat intelligence platforms.
7 merged pull requests
4 repositories
MISP/MISP
Added TweetFeed and phishunt to the MISP default feed list.
MISP/misp-modules
Added TweetFeed and phishunt lookup modules (expansion and hover).
yeti-platform/yeti
Added the phishunt feed and moved the TweetFeed feed out of the deprecated feeds.
OpenCTI-Platform/connectors
There is a TweetFeed connector for OpenCTI.
2015 - 2019
 Universidad de Sevilla
Master's Degree in Telecommunications Engineering
Advanced study of telecommunications networks and systems, including network architecture, signal processing, wireless communications and network security.
2011 - 2015
Universidad de SevillaBachelor's Degree in Telecommunications Engineering
Foundations in telecommunications engineering, computer science and software development.
 GIAC Security Essentials (GSEC) / SANS SEC401Badge
 MITRE ATT&CK Defender™ - Fundamentals Badge TrainingBadgeMITRE ATT&CK Defender™ - Cyber Threat Intelligence Certification TrainingBadgeMITRE ATT&CK Defender™ - SOC Assessments Certification TrainingBadge
 CrowdStrike FHT 201: Intermediate Falcon Platform for RespondersCrowdStrike FHT 202: Intermediate Falcon Platform for Hunters
 Splunk 7.x Fundamentals
 Claude Code in Action (Anthropic)BadgeClaude Code 101 (Anthropic)BadgeIntroduction to agent skills (Anthropic)Badge
 Security Engineering on AWSArchitecting on AWS - AcceleratorAWS Technical Essentials
 Penetration Testing and Ethical Hacking (Cybrary)
 Python for Offensive PenTest (Udemy)
 ITIL FoundationBadge
 On TV3
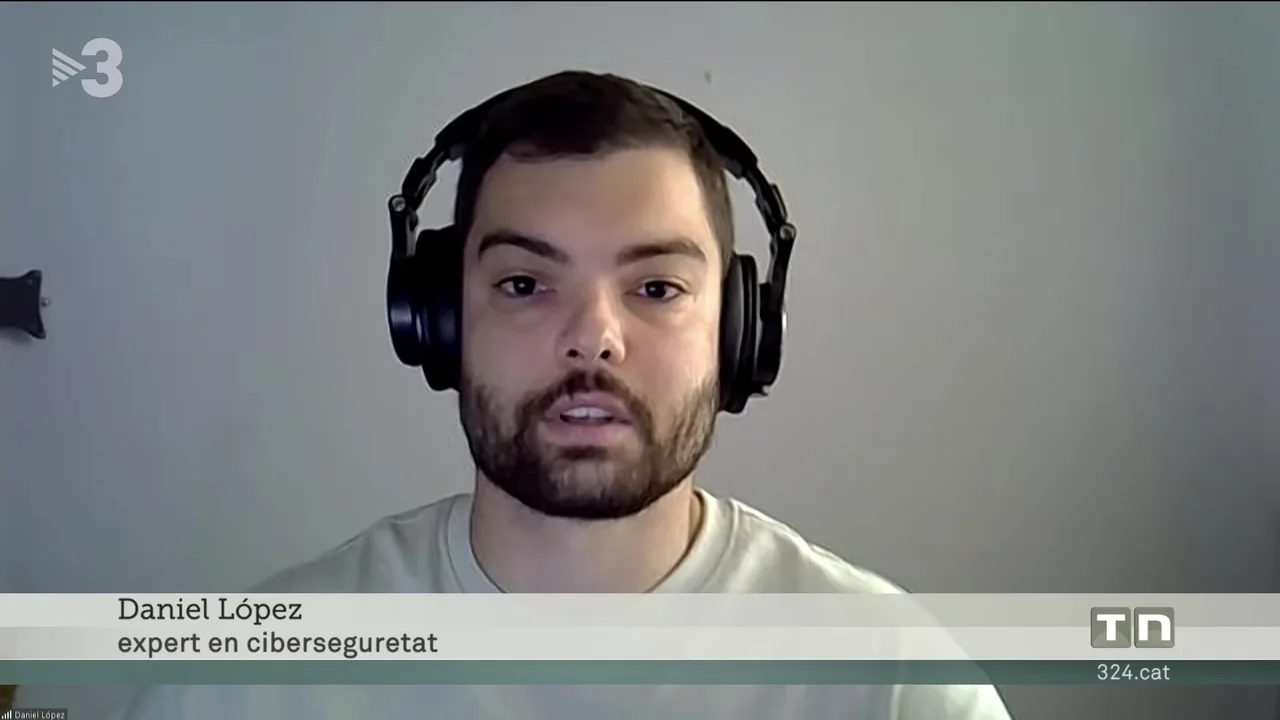
 TV3 midday news
Two appearances on the midday news of TV3.
Watch from 32:15 (opens in a new tab) Watch from 27:48 (opens in a new tab)

In an interview, I explained how Telegram phishing services work, with paid anti-blocking extras and ready-made target lists. I linked a Spanish Tax Agency SMS scam to the kit used against delivery firms.
elconfidencial.com (opens in a new tab)
My tweet is the source for this post, which uses my SMS sample and code screenshot. I also noted that low-skill criminals can easily get the ready-made kits, which use Telegram.
ESET blog (opens in a new tab)
The story starts from my tracking of dozens of fake Correos parcel-tracking sites. Their code shows that several share one kit that sends stolen credentials to Telegram bots, and the article uses my screenshots.
genbeta.com (opens in a new tab)
This guide to tax-season scams cites my warning about fake tax-refund SMS. It also embeds my tweet on new fake Spanish Tax Agency sites, one of which sends stolen data through Telegram.
elcorreo.com (opens in a new tab)
Based on my Twitter thread, the article shows how fake Correos sites share one phishing kit. It embeds my tweets and ends with the list of fake domains I collected.
mundodeportivo.com (opens in a new tab)
This post presents phishunt.io, the site I built to find and monitor suspected phishing websites, and its three sections: suspicious sites, new domain registrations and phishing kits.
derechodelared.com (opens in a new tab)
On Twitter, I reported that scammers used the live chats of Wimbledon interview videos on YouTube to spread malware and crypto-scam links. The article cites and embeds my tweet.
20minutos.es (opens in a new tab)
I uncovered this campaign on Jul. 9, 2022, and the article embeds my two tweets about it. Another researcher replied to my finding and linked the malware to Raccoon Stealer v2.
escudodigital.com (opens in a new tab)As the person behind phishunt.io, I am cited for showing how criminals kept adding hacked websites to host a fake FedEx app. The app was an Android banking trojan spread through SMS links.
ESET blog (opens in a new tab)
According to the post, I was the first to warn on Twitter about this SMS campaign, which sent users to a fake FedEx site. It embeds my tweet of Feb. 11, 2021.
hispasec.com (opens in a new tab)The post follows a crypto scam from a spam email to a fake investment platform. It names me among the researchers who had warned for weeks about fake celebrity arrest ads, and links my tweet.
ESET blog (opens in a new tab)
The author reverse-engineers a fake Android MetaMask app that sends the wallet recovery phrase to the attackers. The post says I first identified the app, and links my tweet.
@themalwarebug - medium.com (opens in a new tab)From Apr. 9, 2023, I tracked fake versions of the MetaMask app for Android, and the post links my tweet. My details show that the criminals copied the official website almost exactly.
ESET blog (opens in a new tab)
TweetFeed, my open feed, is one of the open-source threat feeds benchmarked in this post. Both TweetFeed lists were first to report over 90% of their indicators, and only about a quarter overlapped with other feeds.
silentpush.com (opens in a new tab)You can reach me by email, on LinkedIn or on X.